Information Security · Governance & Compliance · Critical Infrastructure
Cyber Security
The regulation keeps arriving. The audits keep coming. A policy on its own protects nobody — what protects an organisation is a process people actually follow. That is what gets built here.
Information Security Governance & Compliance
Establishing and managing information security governance. Requirements arrive as documents; they have to leave as processes — with owners, evidence, and a place in everyday work.
- NIS2 readiness and compliance tracking
- KRITIS and BSI IT-Grundschutz
- GDPR-related compliance
- Development and improvement of security policies
ISO 27001
Support in building and running an information security management system to ISO 27001, from the initial assessment through to the state your organisation needs to reach before an external audit.
Gap Analysis, Remediation & Audit Preparation
Structured gap analysis against the relevant security and compliance requirements, including assessment of each gap and definition of concrete measures to close it.
- Follow-up of agreed remediation measures until they are done
- Risk analysis
- Audit preparation, coordination and preparation of required evidence and documentation
Substantial gains in maturity within months are achievable (e.g. from 1.45 to 3.09 in eight months). How fast depends on the starting point, available resources and the involvement of the organisation.
Project Management for Cyber Security Initiatives
Delivery support for security programmes, where governance, coordination and follow-through decide whether the work lands.
- Coordination of rollout and onboarding of security, monitoring and analytics tools through external service providers
- Management and steering committee reporting
- Risk and quality management
- Stakeholder and service-provider management
Vulnerability Management
Vulnerability management and vulnerability assessment, together with security monitoring — not as a one-off scan, but as a process with owners, priorities and a closing loop.
Supply Chain Security
A supplier’s weaknesses become yours the moment they connect. Structured review of service-provider contracts against defined security and compliance requirements, drawing on experience developing a Service Provider Security Policy and a standardised checklist for assessing such contracts.
Business Continuity
Backup and recovery workstreams and the continuity thinking around them: what has to keep running, how quickly it has to come back, and who decides in the moment.
Security Awareness Programmes
User awareness training built as an ongoing programme rather than an annual obligation — because the people using the systems are the control that works every day.
- Hands-on live training for staff, delivered remotely as online sessions
- Training material and session documentation
- Attendance records and evidence suitable for audits
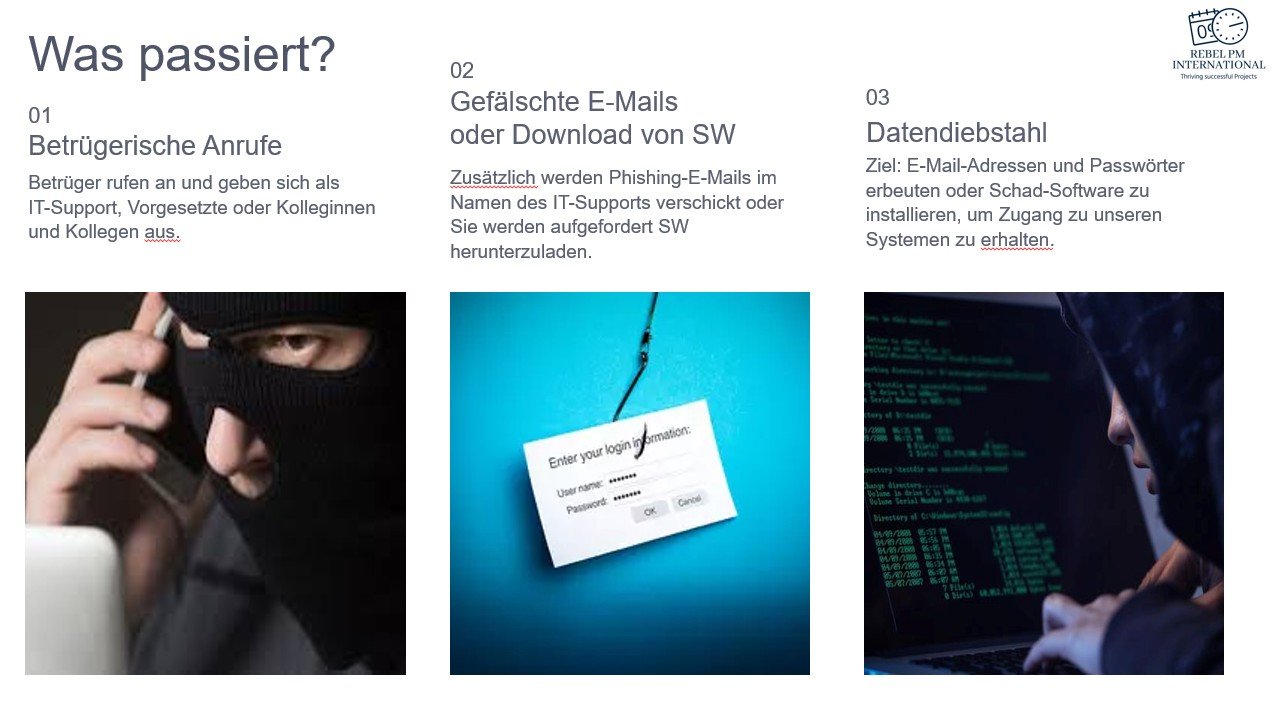
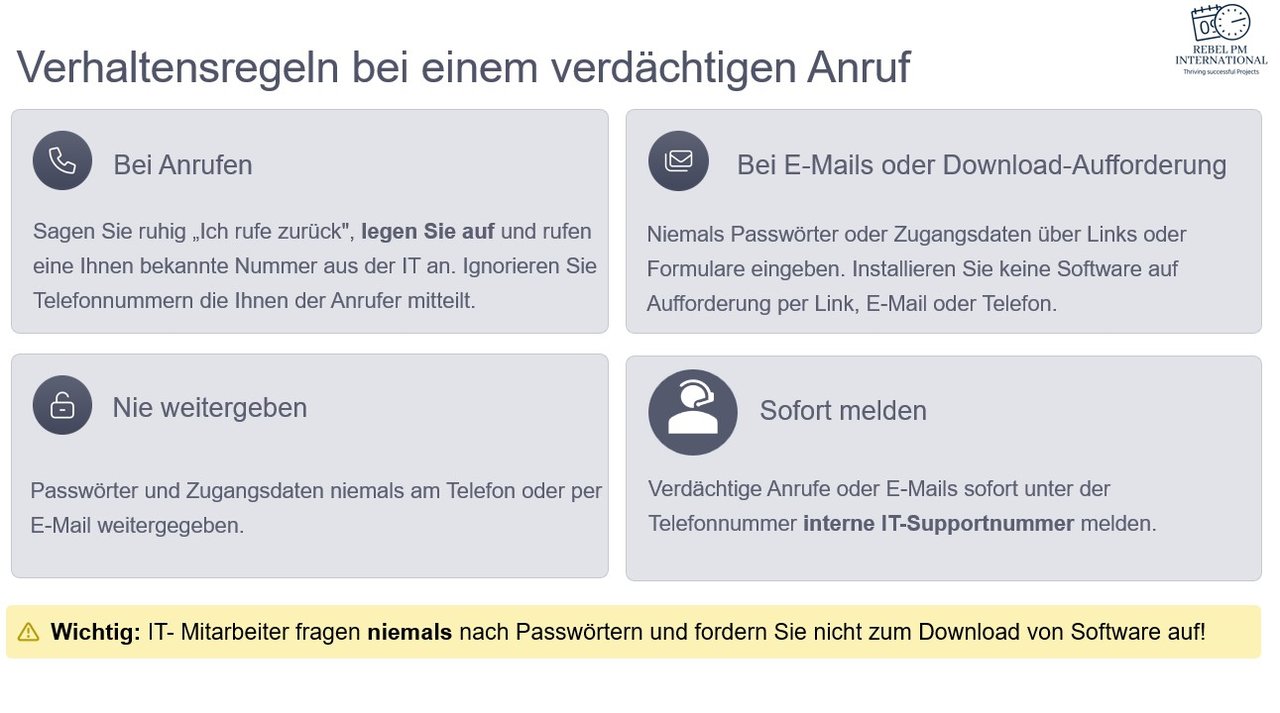
- Tailored awareness training for non-technical employees: Practical, accessible training on phishing, fraudulent calls and fake IT support.
CISO Sparring
A counterpart for security leaders who have to make the call themselves: someone to test the reasoning against, from outside the organisation and without an agenda in it.
Markets and sector experience
Compliance consulting is offered exclusively for organisations operating in the EU and UK markets.
Particular experience includes healthcare, the public sector and critical infrastructure. Further project experience covers financial services, insurance, automotive, telecommunications, public transportation and enterprise IT.
The service covers consulting, governance and project-delivery support. Rebel PM International does not provide legal advice and does not act as a certification body.