Security Awareness · Phishing · Social Engineering
Security Awareness Training for Staff
No off-the-shelf course. Practical security awareness training, built around your organisation, your people and the risks you actually face.
Security Awareness Training for Staff
The attacks that actually land do not target the technology. They target people under time pressure. Those are the situations the training rehearses.
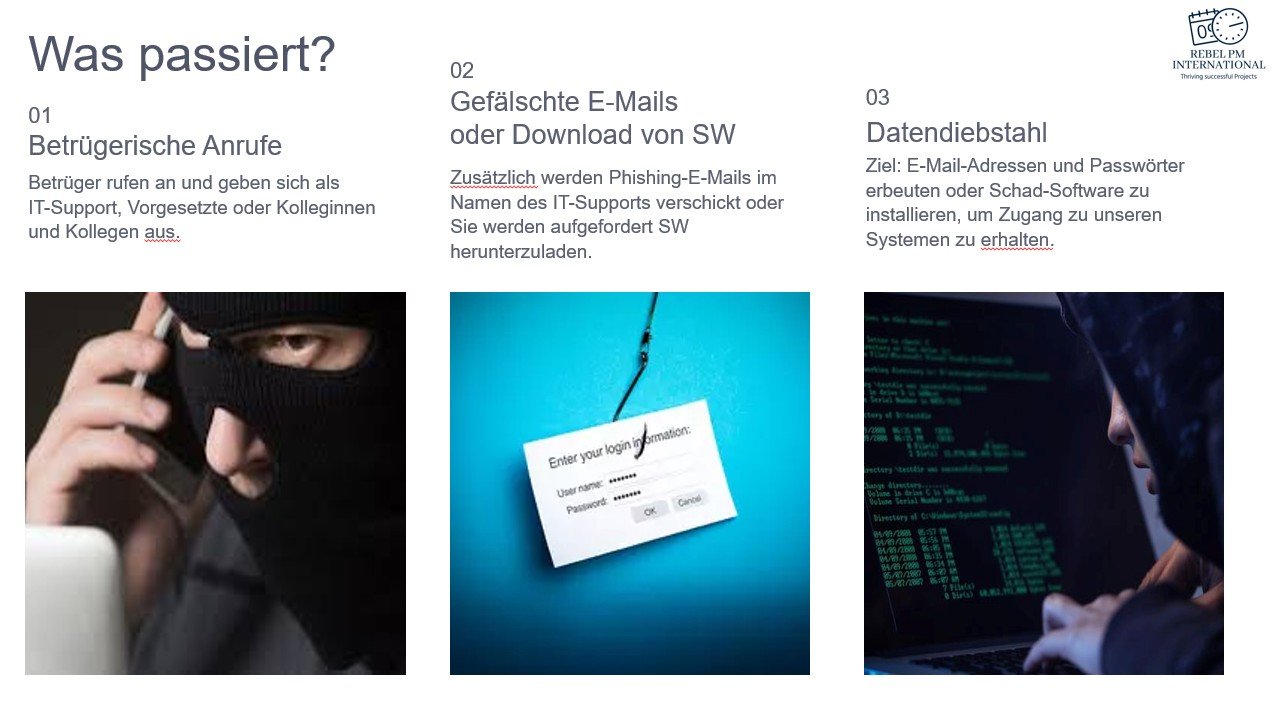
- Phishing and forged email
- Social engineering
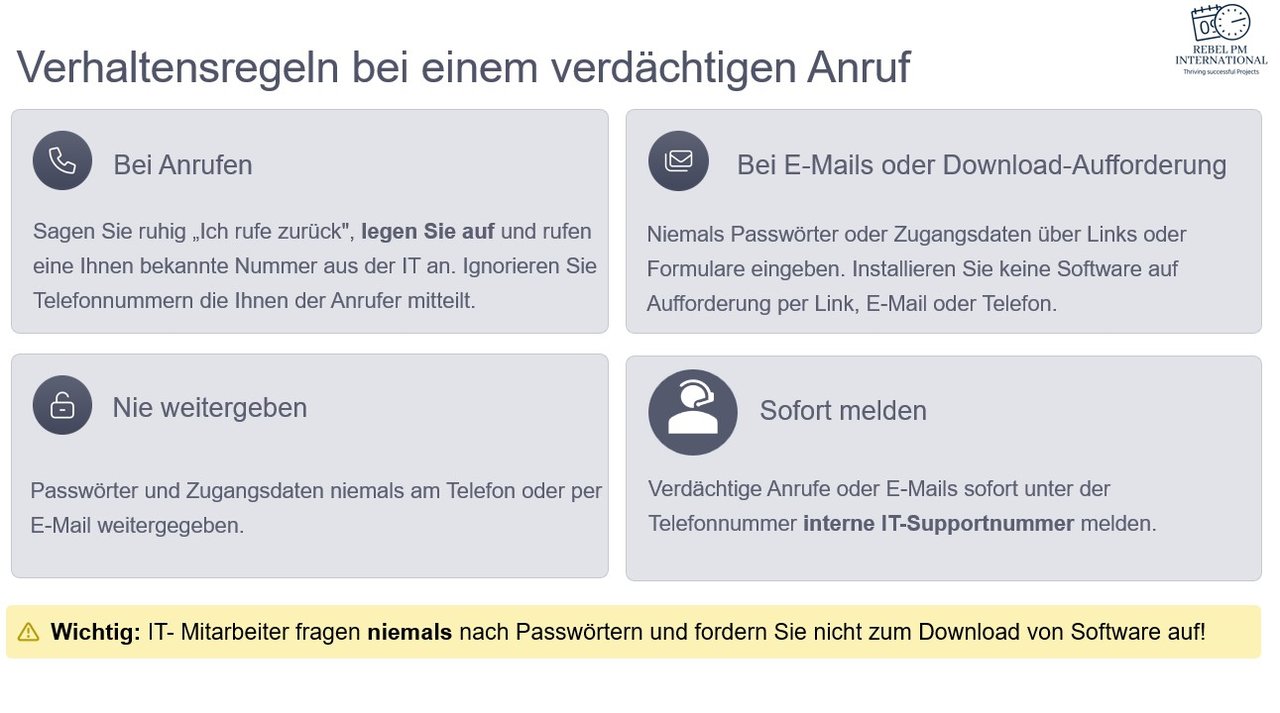
- Fake IT support
- Fraudulent calls
- Password and account security
Security Awareness Analysis: built around your organisation
Your sector, your processes, the attack scenarios you realistically face, the policies you already have and real examples from your own organisation all go into the session.
The difference shows: people recognise the situation instead of hearing an abstract rule that nobody applies on a busy Tuesday.
Security Awareness Training for Leadership
Separate content for management and for people carrying particular responsibility. Leaders are a more rewarding target, they make the decisions — and under NIS2 they are required to be trained themselves.
NIS2 Awareness: a training obligation
Awareness training as a component of a NIS2 security programme, including documentation and attendance records.
A Look at the Material
Four slides from an awareness session on fraudulent calls and fake IT support.
Security awareness training: two options
The scope follows the size of your organisation and how much is at stake.
| Item | Compact | Comprehensive |
|---|---|---|
| Suited to | smaller organisations / manageable structures | more complex organisations |
| Analysis | questionnaire + 1–2 interviews | in-depth analysis |
| Risks specific to your organisation | included | included |
| Attack scenarios built for your context | included | included |
| Tailored training content | included | included |
| Live session | included | included |
| Documentation / attendance records | included | included |
| Findings report | concise | detailed |
| Indicative price | from €2,500 net | from €4,500 net |
Scroll the table sideways to see both options.
No long standard courses. The session itself runs 30 to 60 minutes. The effort sits in the preparation — so that your staff learn exactly what matters for your organisation.
Frequently asked questions
What does a tailored security awareness training cost?
There is no off-the-shelf course here. The content is matched to your organisation, your actual risks, your processes and the audience in the room.
Before the training we work through the relevant attack scenarios and organisational specifics with you. On that basis we build a compact, practical live session for your staff or your leadership team.
As an indication: the Compact option starts at €2,500 net and the Comprehensive option at €4,500 net. The exact figure depends on the depth of the pre-analysis and the number of audiences.
How long does the training take?
30 to 60 minutes. That is deliberate: an awareness session that runs half a day has lost the room after twenty minutes.
The effort sits in the preparation. Because the content is cut to your organisation beforehand, what is left in the session is only what actually applies to your staff — and that fits inside an hour.
How is the training adapted to our organisation?
It starts with a structured pre-analysis. In one or two interviews we go through your sector, your processes, the attack scenarios you realistically face and the policies you already have.
Real examples from your organisation go into the session. That is what makes the difference: people recognise the situation instead of hearing an abstract rule.
Can the training be delivered remotely?
Yes. The training is delivered as a live online session (no recording), followed by a question-and-answer session.
In which language is the training delivered?
The training can be delivered in German or English.
Non-technical staff should be trained in the language of their country, their public body or their organisation, because the material is easier to follow that way.
Which employees should attend?
Broadly, everyone who works with email, the phone and company data. Attacks rarely target the IT department; they target finance, reception, assistants and sales.
Particular attention goes to people without a technical background — they are often the target and get the least support.
Is there a separate session for managers?
Yes. Management and people carrying particular responsibility get their own content.
The reason is simple: leaders are a more rewarding target, they carry the accountability for decisions, and under NIS2 they are required to be trained themselves.
What role does security awareness play under NIS2?
NIS2 explicitly requires cyber-security training, including for the management body. Awareness is therefore part of the obligation rather than an optional extra.
The training can be run as a component of a NIS2 security programme, with documentation and attendance records. More on the NIS2 Compliance page.
Do we receive attendance records and documentation?
Yes. Every training comes with the material, a record of the session and attendance evidence suitable for an audit.
The Comprehensive option adds a findings report with recommendations.